Satish Laxminarayanan
CISO & Advisor
Independent
CFP opens 12 November
13 Jan 2027 · 8:00 AM – 6:00 PM ET · Online · Free
One day. One room. The whole software supply chain — pipelines, AI, agentic systems, quantum readiness, vendor risk, and hardware — with 85+ speakers in a reviewed room. Nothing published afterwards, so people can be specific.
Doors open in
🔴 Call for speakers goes live Nov 12
Speakers
85+ speakers expected. Confirmed names below — more announcements as the CFP fills out.
CISO & Advisor
Independent
Chief Trust & Resilience Officer
Firstsource
CISO & Head of IT Infrastructure
Chimera Investment Corporation
Former Chief Information Security Officer
Ziff Davis
Partner & Co-Founder
The CISO Law Firm
Vice President, Security Engineering
Tekion Corp
Chief Data & AI Officer
TE Connectivity
Co-Founder & Managing Director
MitKat Advisory
VP & Head of Cyber Security, North America & Defense
Rolls-Royce
CISO
Shake Shack
Senior Information Security Architect
Global Payments
CISO
Justworks
Principal Cybersecurity Engineering & Innovation Architect
Lumen Technologies
Senior Cybersecurity and Risk Management Specialist
Mizuho
Product Security, Risk, Compliance and Privacy
Informatica
Speakers
To be announced
Key topics
Six tracks across software pipelines, AI and agentic systems, quantum readiness, vendor risk, hardware, and the policy that binds them.
SBOM, CI/CD hardening, open source risk, signing and attestation — the path from source to production stays visible and tamper-evident.
Models, datasets, AIBOM, AgBOM, MCP servers and agent identity — provenance when the artifact is weights, and when software starts acting on your behalf.
QBOM, PQC migration, crypto agility — inventorying algorithms and planning the cutover before quantum breaks today’s signatures.
Supplier assurance that survives an audit and a real incident — questionnaires that die, evidence that sticks, and shared accountability.
HBOM, CBOM, firmware, silicon and crypto modules — the physical and cryptographic layers under every software supply chain.
EU CRA, NIS2, secure-by-design pledges, procurement language and the standards bodies writing the next round of requirements.
Partners
Sponsors keep the event free and get clearly-labelled slots of their own. They have no say over the CFP, the judges, who is admitted, or any other session.

More partners to be announced
Why this format
That combination is what lets speakers talk about real incidents — vendors named, configs shown, failures described honestly — instead of sanitised case studies.
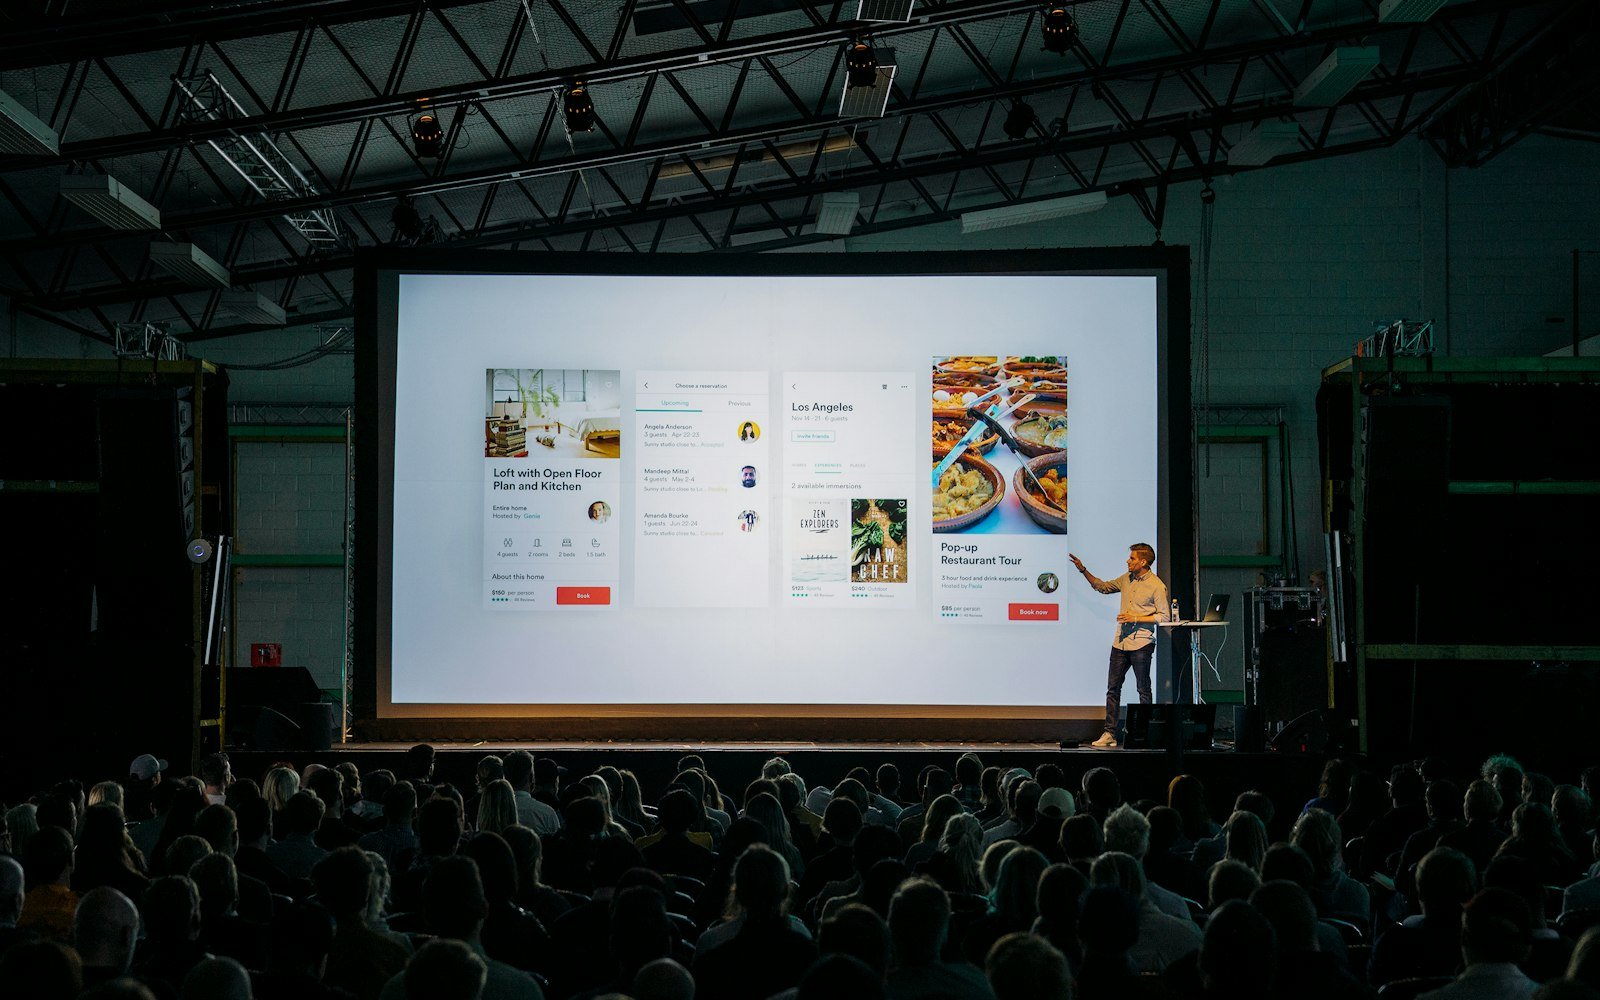
We review every application and balance the room. Practitioners who work this problem are welcome; sales prospecting is not.
Sponsors cover production. Attending is free so the exclusivity is who is in the room — not who can pay.
Sessions are recorded for confirmed attendees only. Nothing is posted publicly, handed to sponsors, or put on YouTube.